Your next security decision starts here with AI-powered Threat Intelligence
*According to Kaspersky ROI Calculation Analysis Report, 2026
Three pillars of efficiency
- Transform intelligence overload into actionable insights
- Gain strategic visibility beyond your environment and build strategy
- Investigate sophisticated threats, validate findings and access expert insights
Your AI-powered Threat Intelligence Assistant
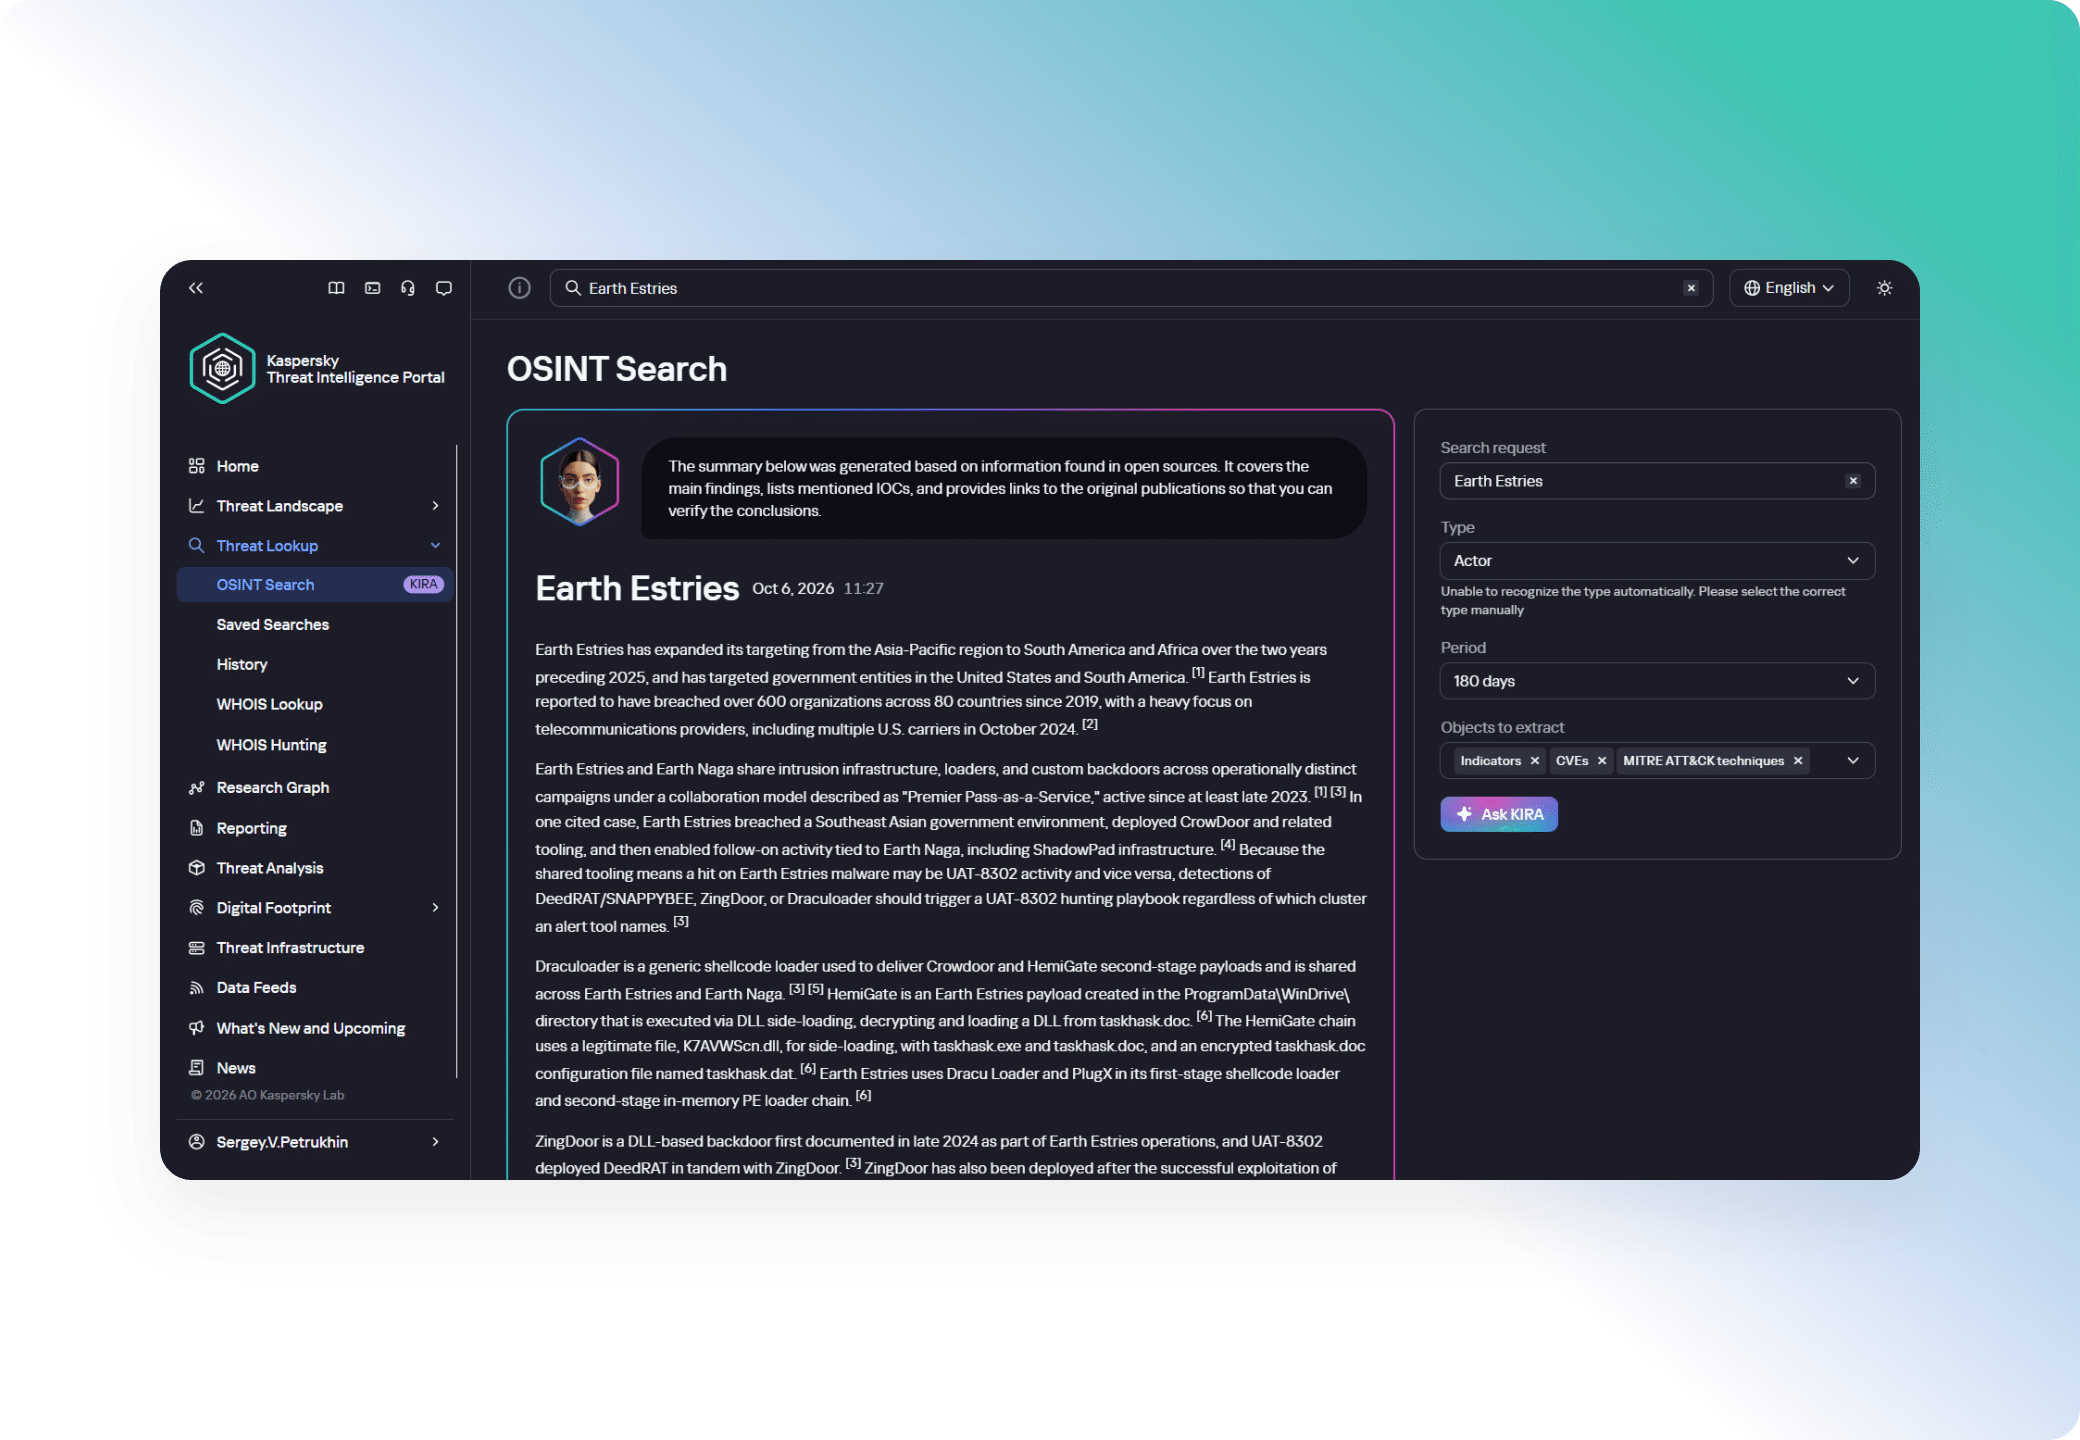
KIRA, Kaspersky Investigation and Response Assistant, helps security teams work faster and more efficiently by bringing AI-powered assistance directly into your daily cybersecurity workflows. For specific use cases, you can connect your preferred third-party AI models.
AI-powered summarization cuts through complex security context so you spend significantly less time reading to understand and more time making informed decisions.
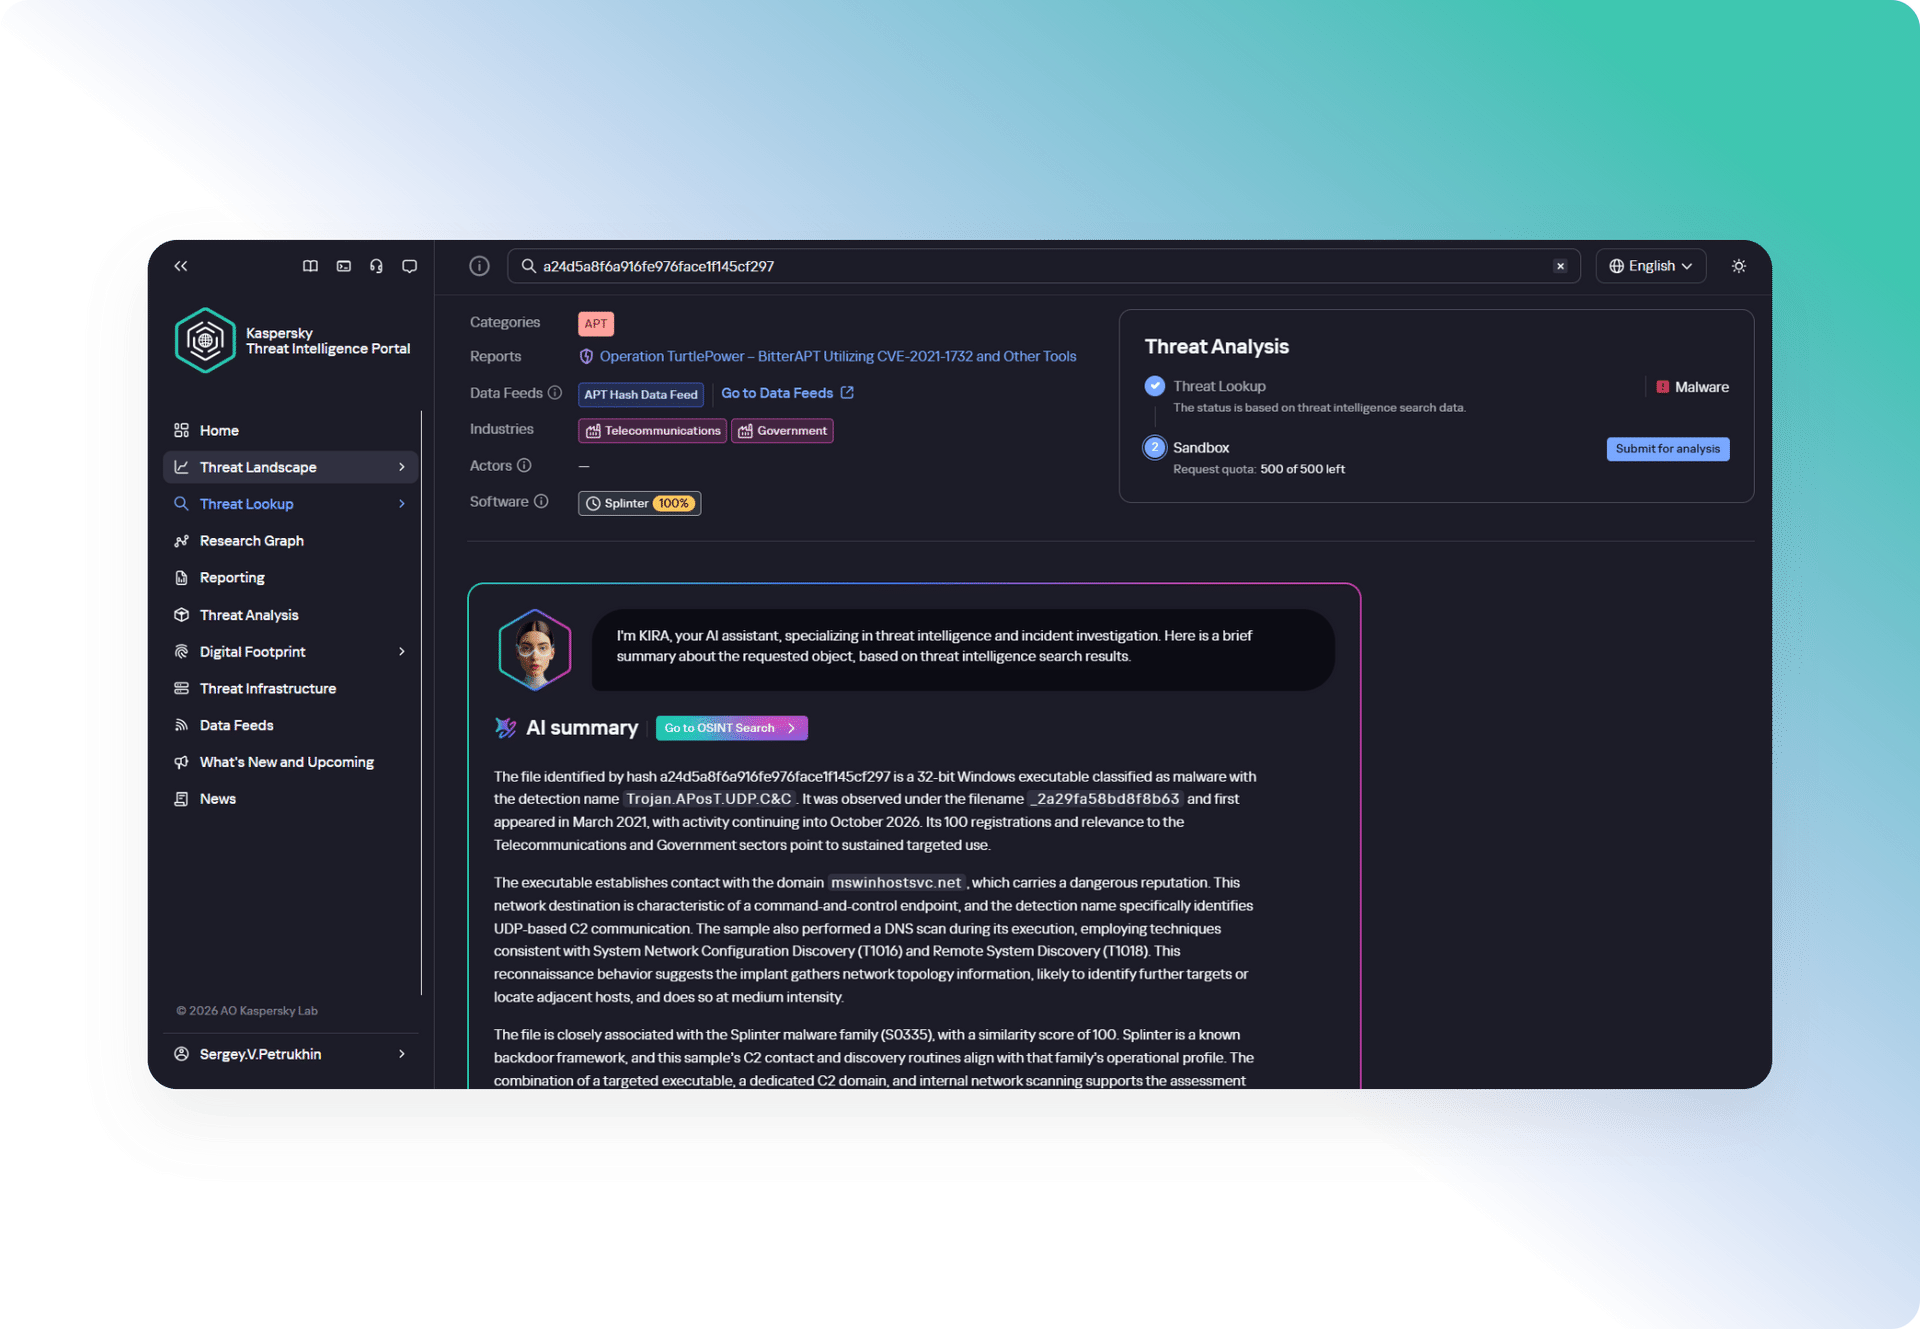
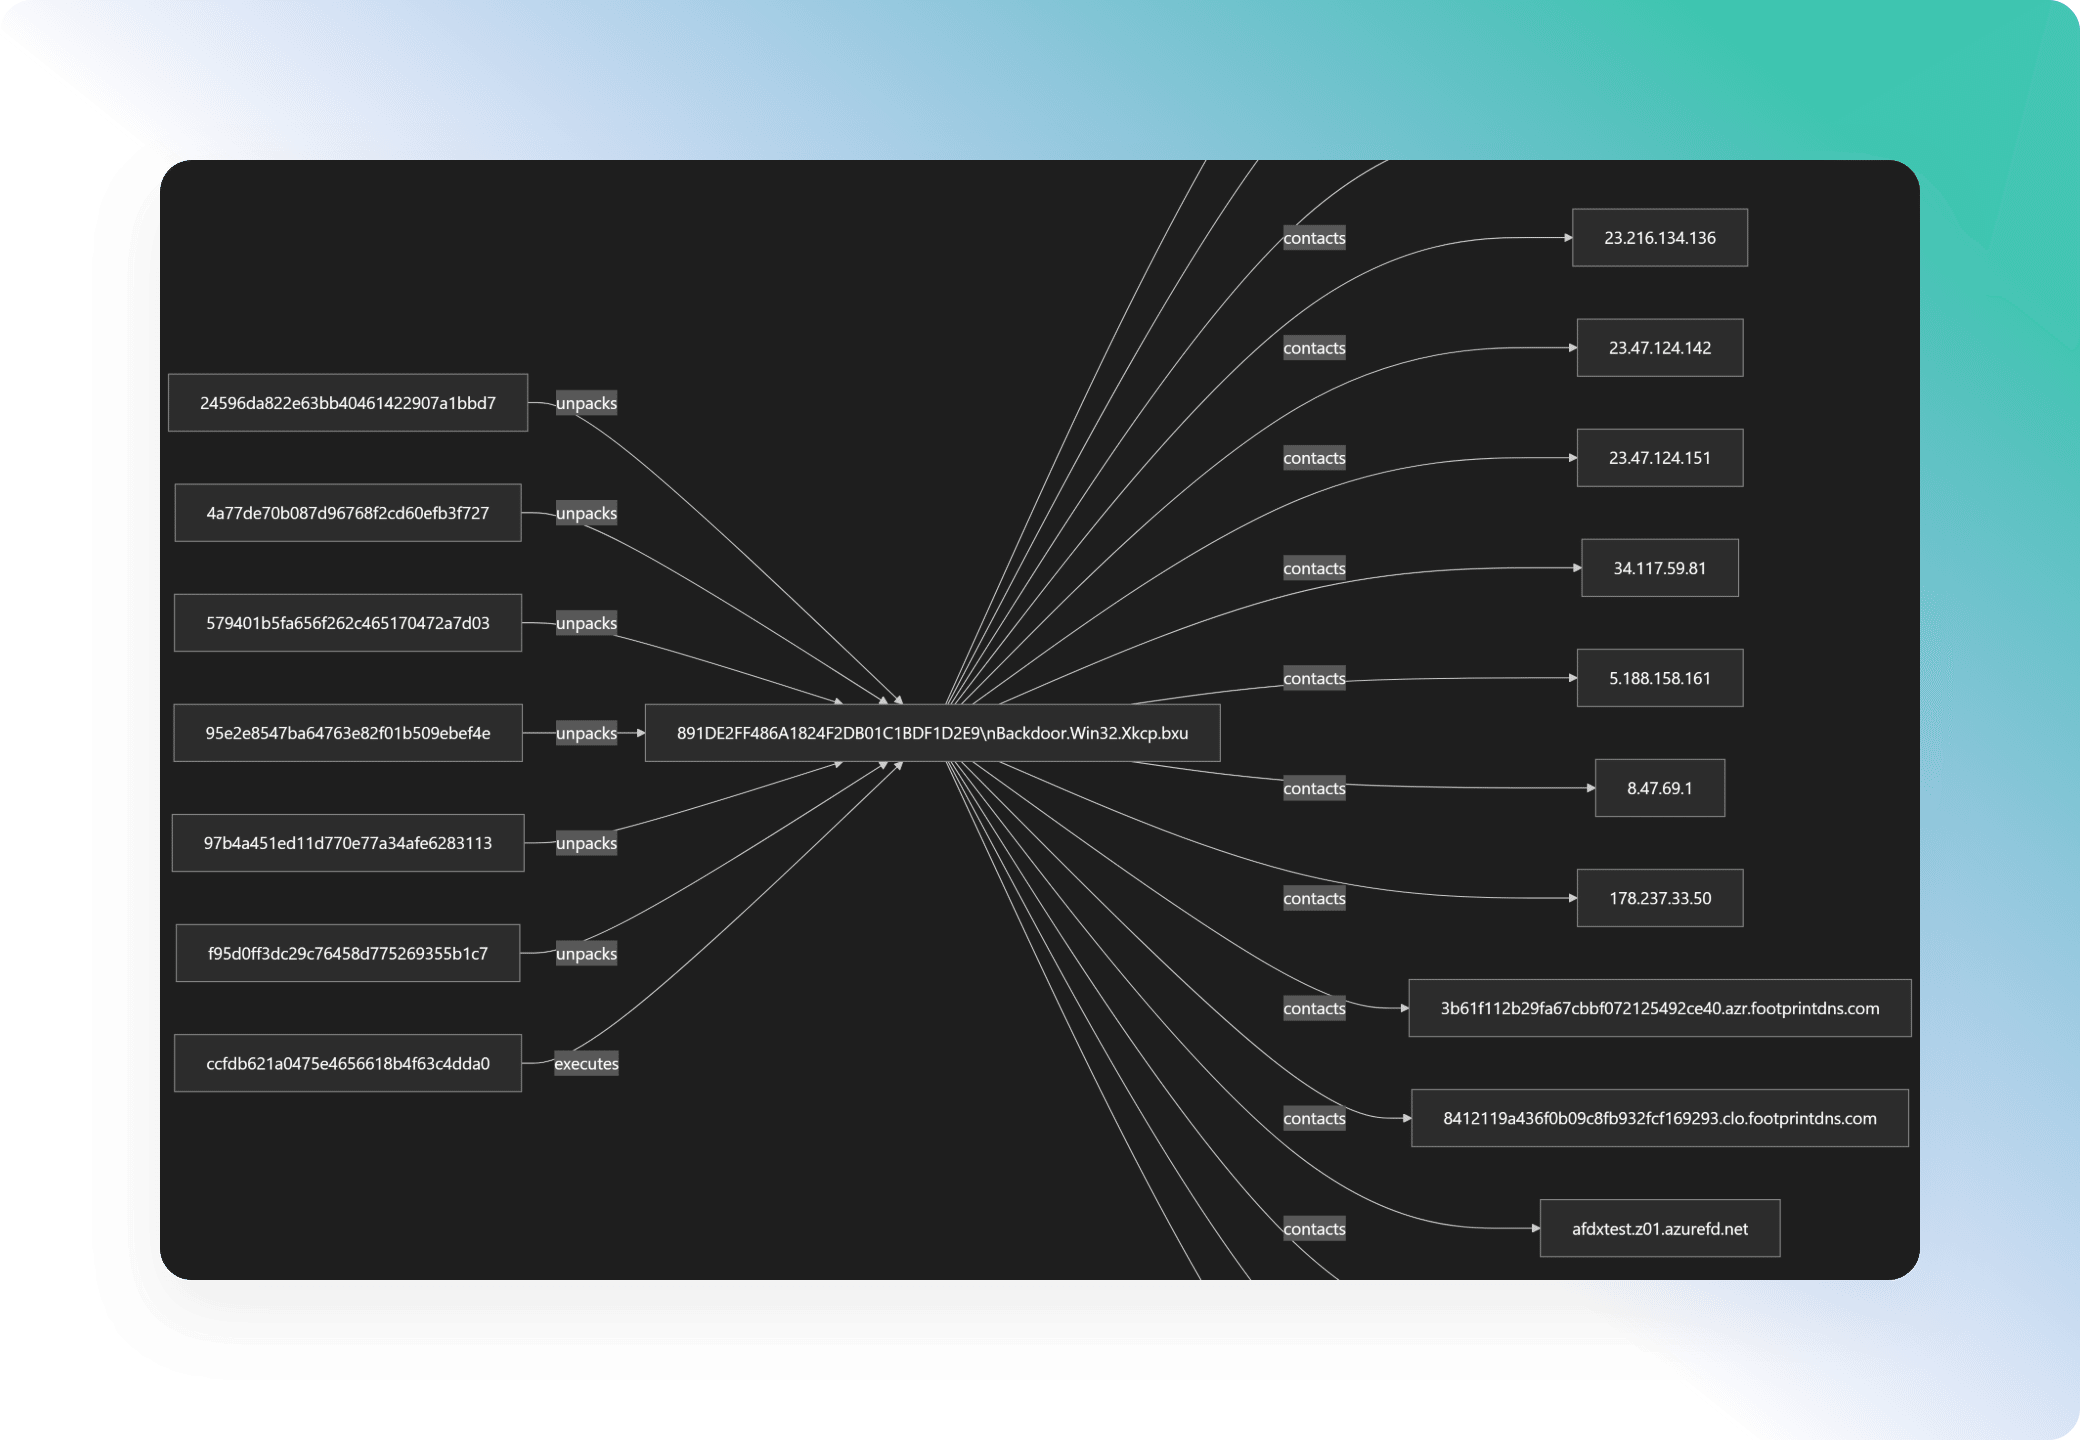
When searching for any object, AI automatically traces its relationships across multiple levels, aggregates the results, and produces a simple, human-readable verdict explaining what was found and why the object was classified in that way.
What used to multiple manual lookups now takes just one.
When searching for any object, AI automatically traces its relationships across multiple levels, aggregates the results, and produces a simple, human-readable verdict explaining what was found and why the object was classified in that way.
What used to multiple manual lookups now takes just one.
Try the Kaspersky Threat Intelligence Portal
Discover how the Kaspersky Threat Intelligence Portal optimizes your SOC processes, incident response and threat hunting by combining expanded AI, advanced tools and trusted independent expertise that makes every investigation more efficient.
ADVANCED TOOLS
Become a threat hunter
Perishable data to support security operations and incident response
Kaspersky Threat Lookup
Access Kaspersky’s complete body of cyberthreat knowledge, along with the connections between related threats.
Kaspersky Threat Intelligence Reporting
Stay ahead of the most relevant, dangerous threats with exclusive access to Kaspersky research and expert threat intelligence.
ADVANCED TOOLS
Become a threat hunter
Perishable data to support security operations and incident response
Kaspersky Threat Lookup
Access Kaspersky’s complete body of cyberthreat knowledge, along with the connections between related threats.

Kaspersky Threat Analysis
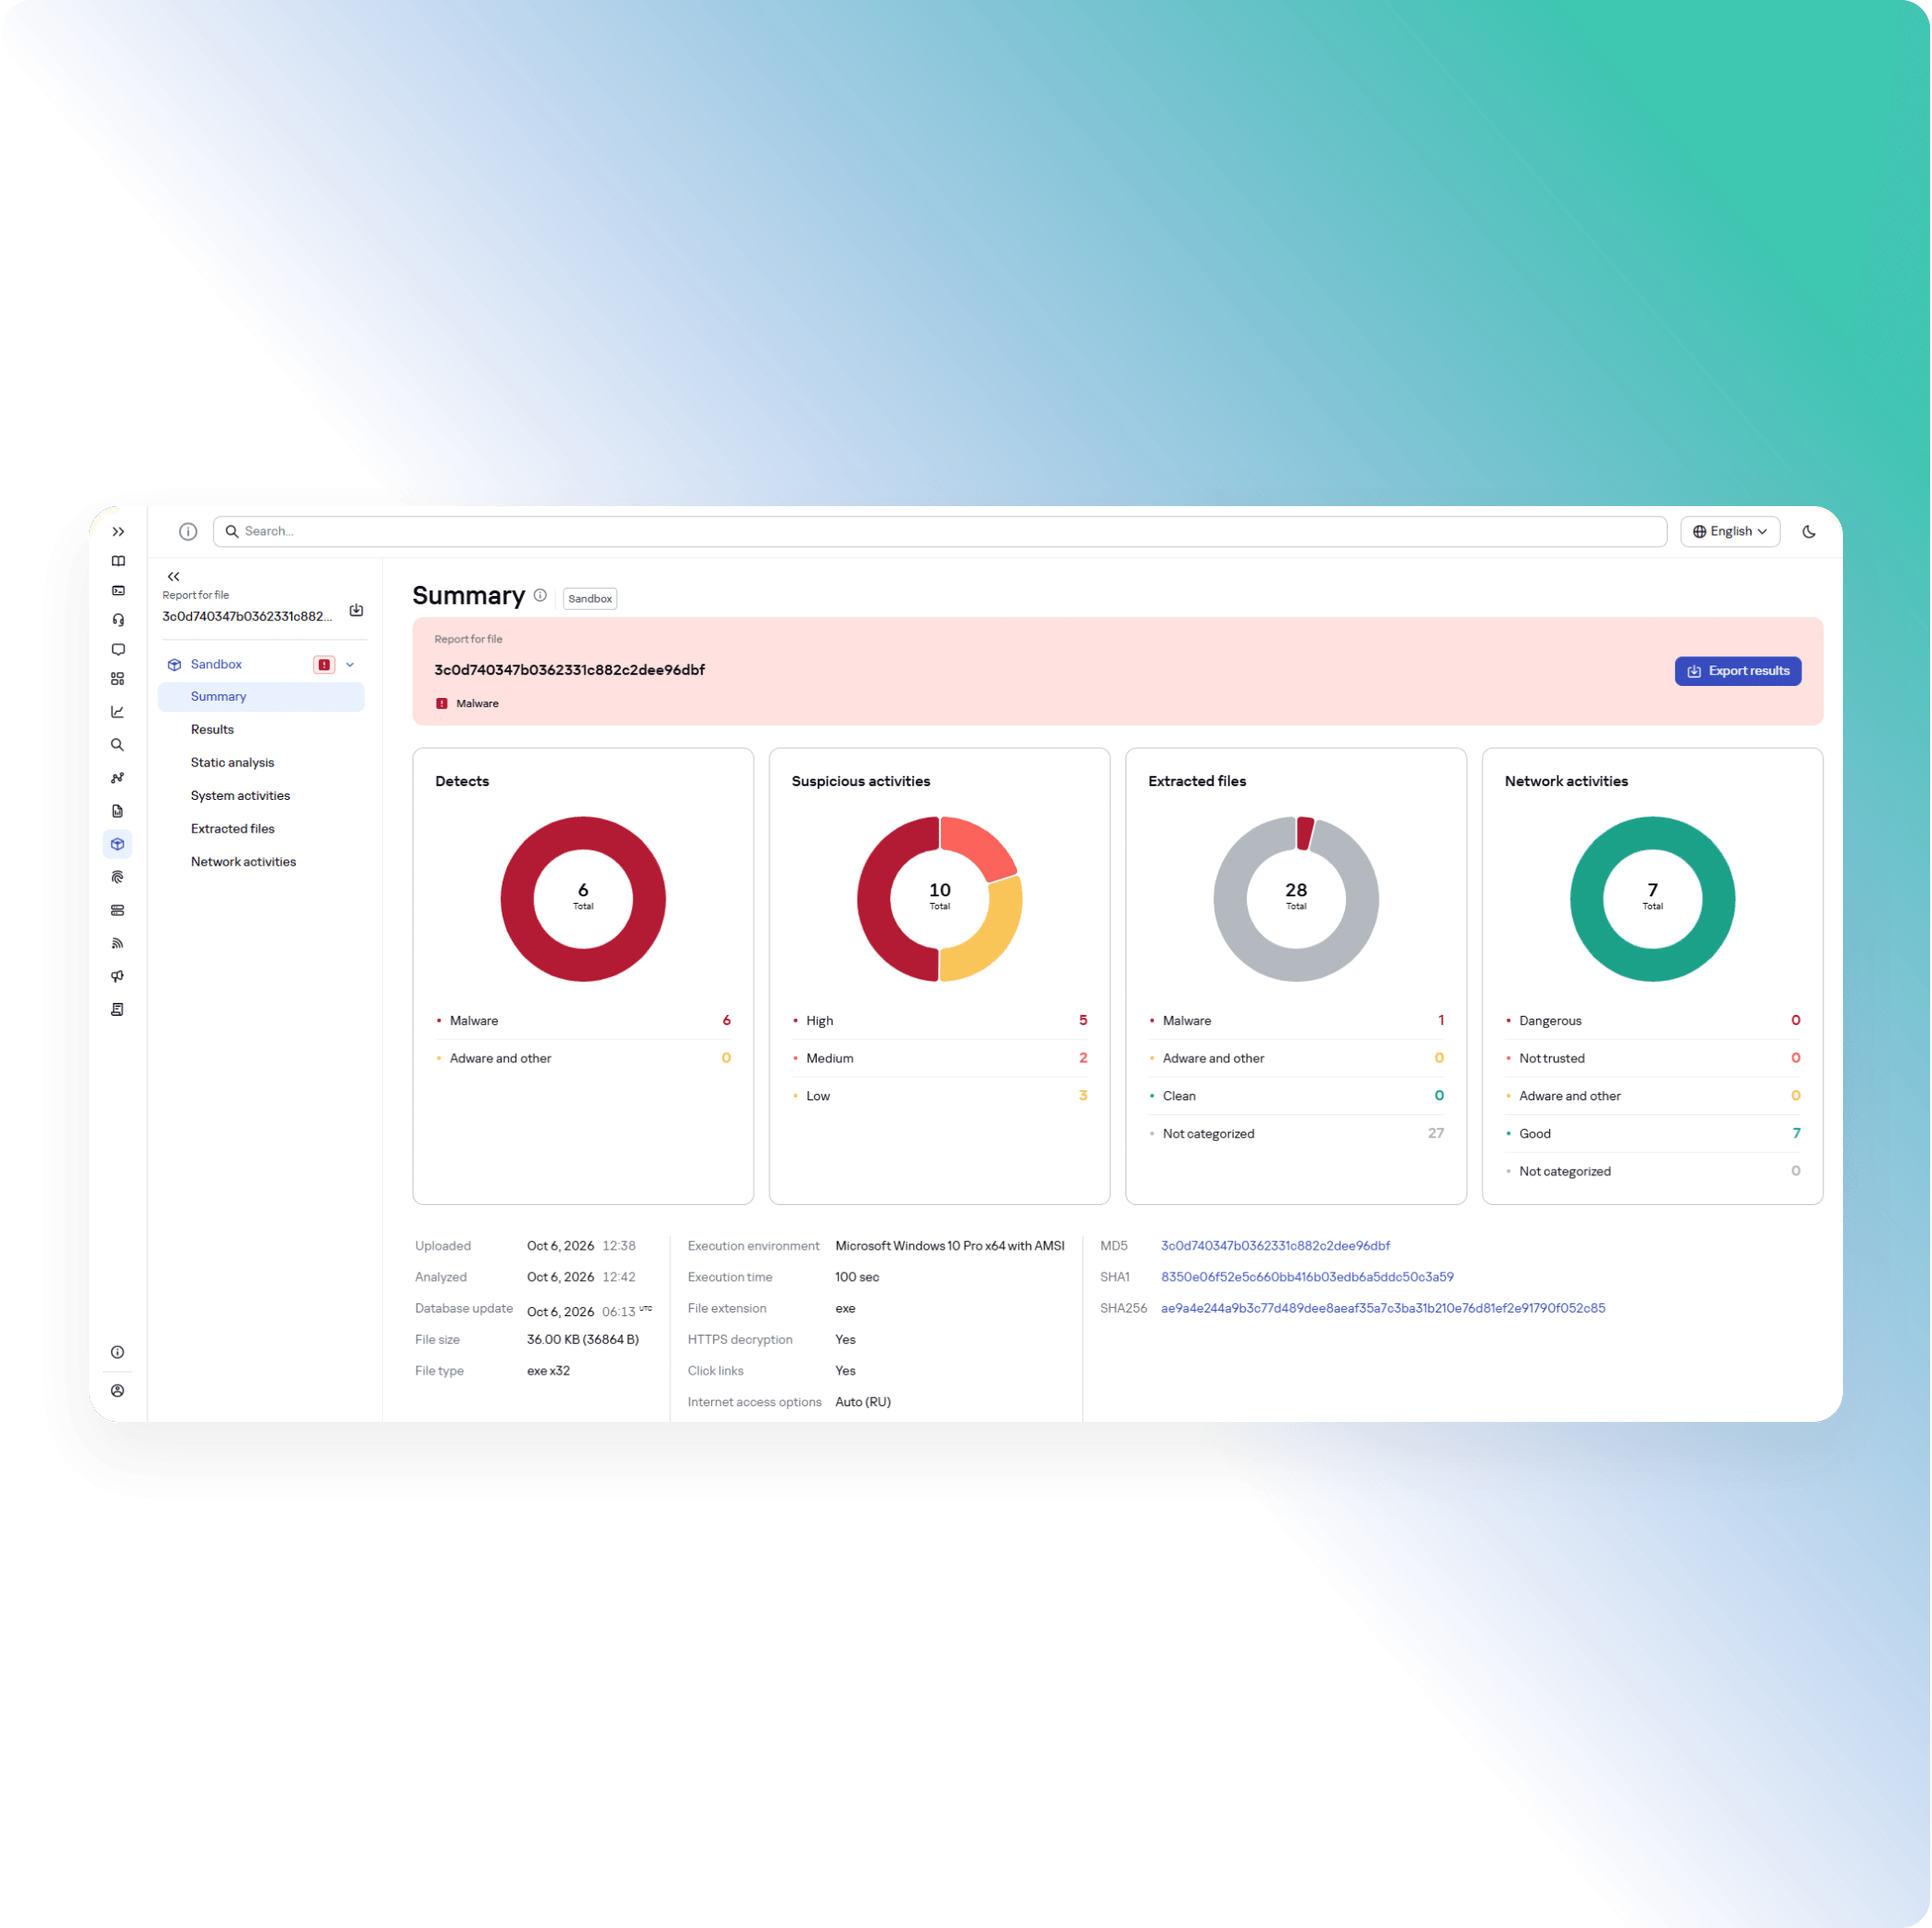
Go beyond surface-level analysis with flexible, multi-layered analysis to detect previously unknown threats in suspicious files.
Kaspersky Threat Intelligence Reporting
Stay ahead of the most relevant, dangerous threats with exclusive access to Kaspersky research and expert threat intelligence.

Kaspersky Digital Footprint Intelligence
Comprehensive monitoring of your corporate digital assets to detect threats to your organization from the surface, deep and dark web.

Kaspersky Brand Monitoring
Detect and mitigate brand abuse, impersonation and other online threats with advanced brand monitoring backed by unique expertise.
ADVANCED TOOLS
Become a threat hunter
Perishable data to support security operations and incident response
Kaspersky Threat Intelligence Reporting
Stay ahead of the most relevant, dangerous threats with exclusive access to Kaspersky research and expert threat intelligence.
Kaspersky Digital Footprint Intelligence
Comprehensive monitoring of your corporate digital assets to detect threats to your organization from the surface, deep and dark web.
Kaspersky Brand Monitoring
Detect and mitigate brand abuse, impersonation and other online threats with advanced brand monitoring backed by unique expertise.
ADVANCED TOOLS
Become a threat hunter
Perishable data to support security operations and incident response

Kaspersky Threat Landscape
A tailored threat landscape reflecting the specific risks, trends and threats relevant to your industry and region.
USE CASES
A Unified Threat Intelligence workflow
Incident Response
Investigate security incidents faster and understand the full context needed to respond effectively.
- Investigate IOCs – enrich IPs, domains, URLs and hashes with context and relationships
- Analyze suspicious files – identify malicious behavior and uncover relevant evidence
- Reconstruct the incident – connect indicators, files and related threats to build a broader picture of the attack
- Prioritize the response – assess the relevance and potential impact of the threat
- Get expert context – understand related sophisticated campaigns and attacker activity
Threat Hunting
Proactively search for hidden threats and uncover malicious activity that may have bypassed existing defenses.
- Search for unknown connections – explore relationships between indicators, infrastructure and threat artifacts
- Validate hunting hypotheses – investigate suspicious files and related samples
- Hunt for emerging threats – identify new threats and activity relevant to your industry and organization
- Extend the hunt externally – investigate exposed assets and compromised accounts
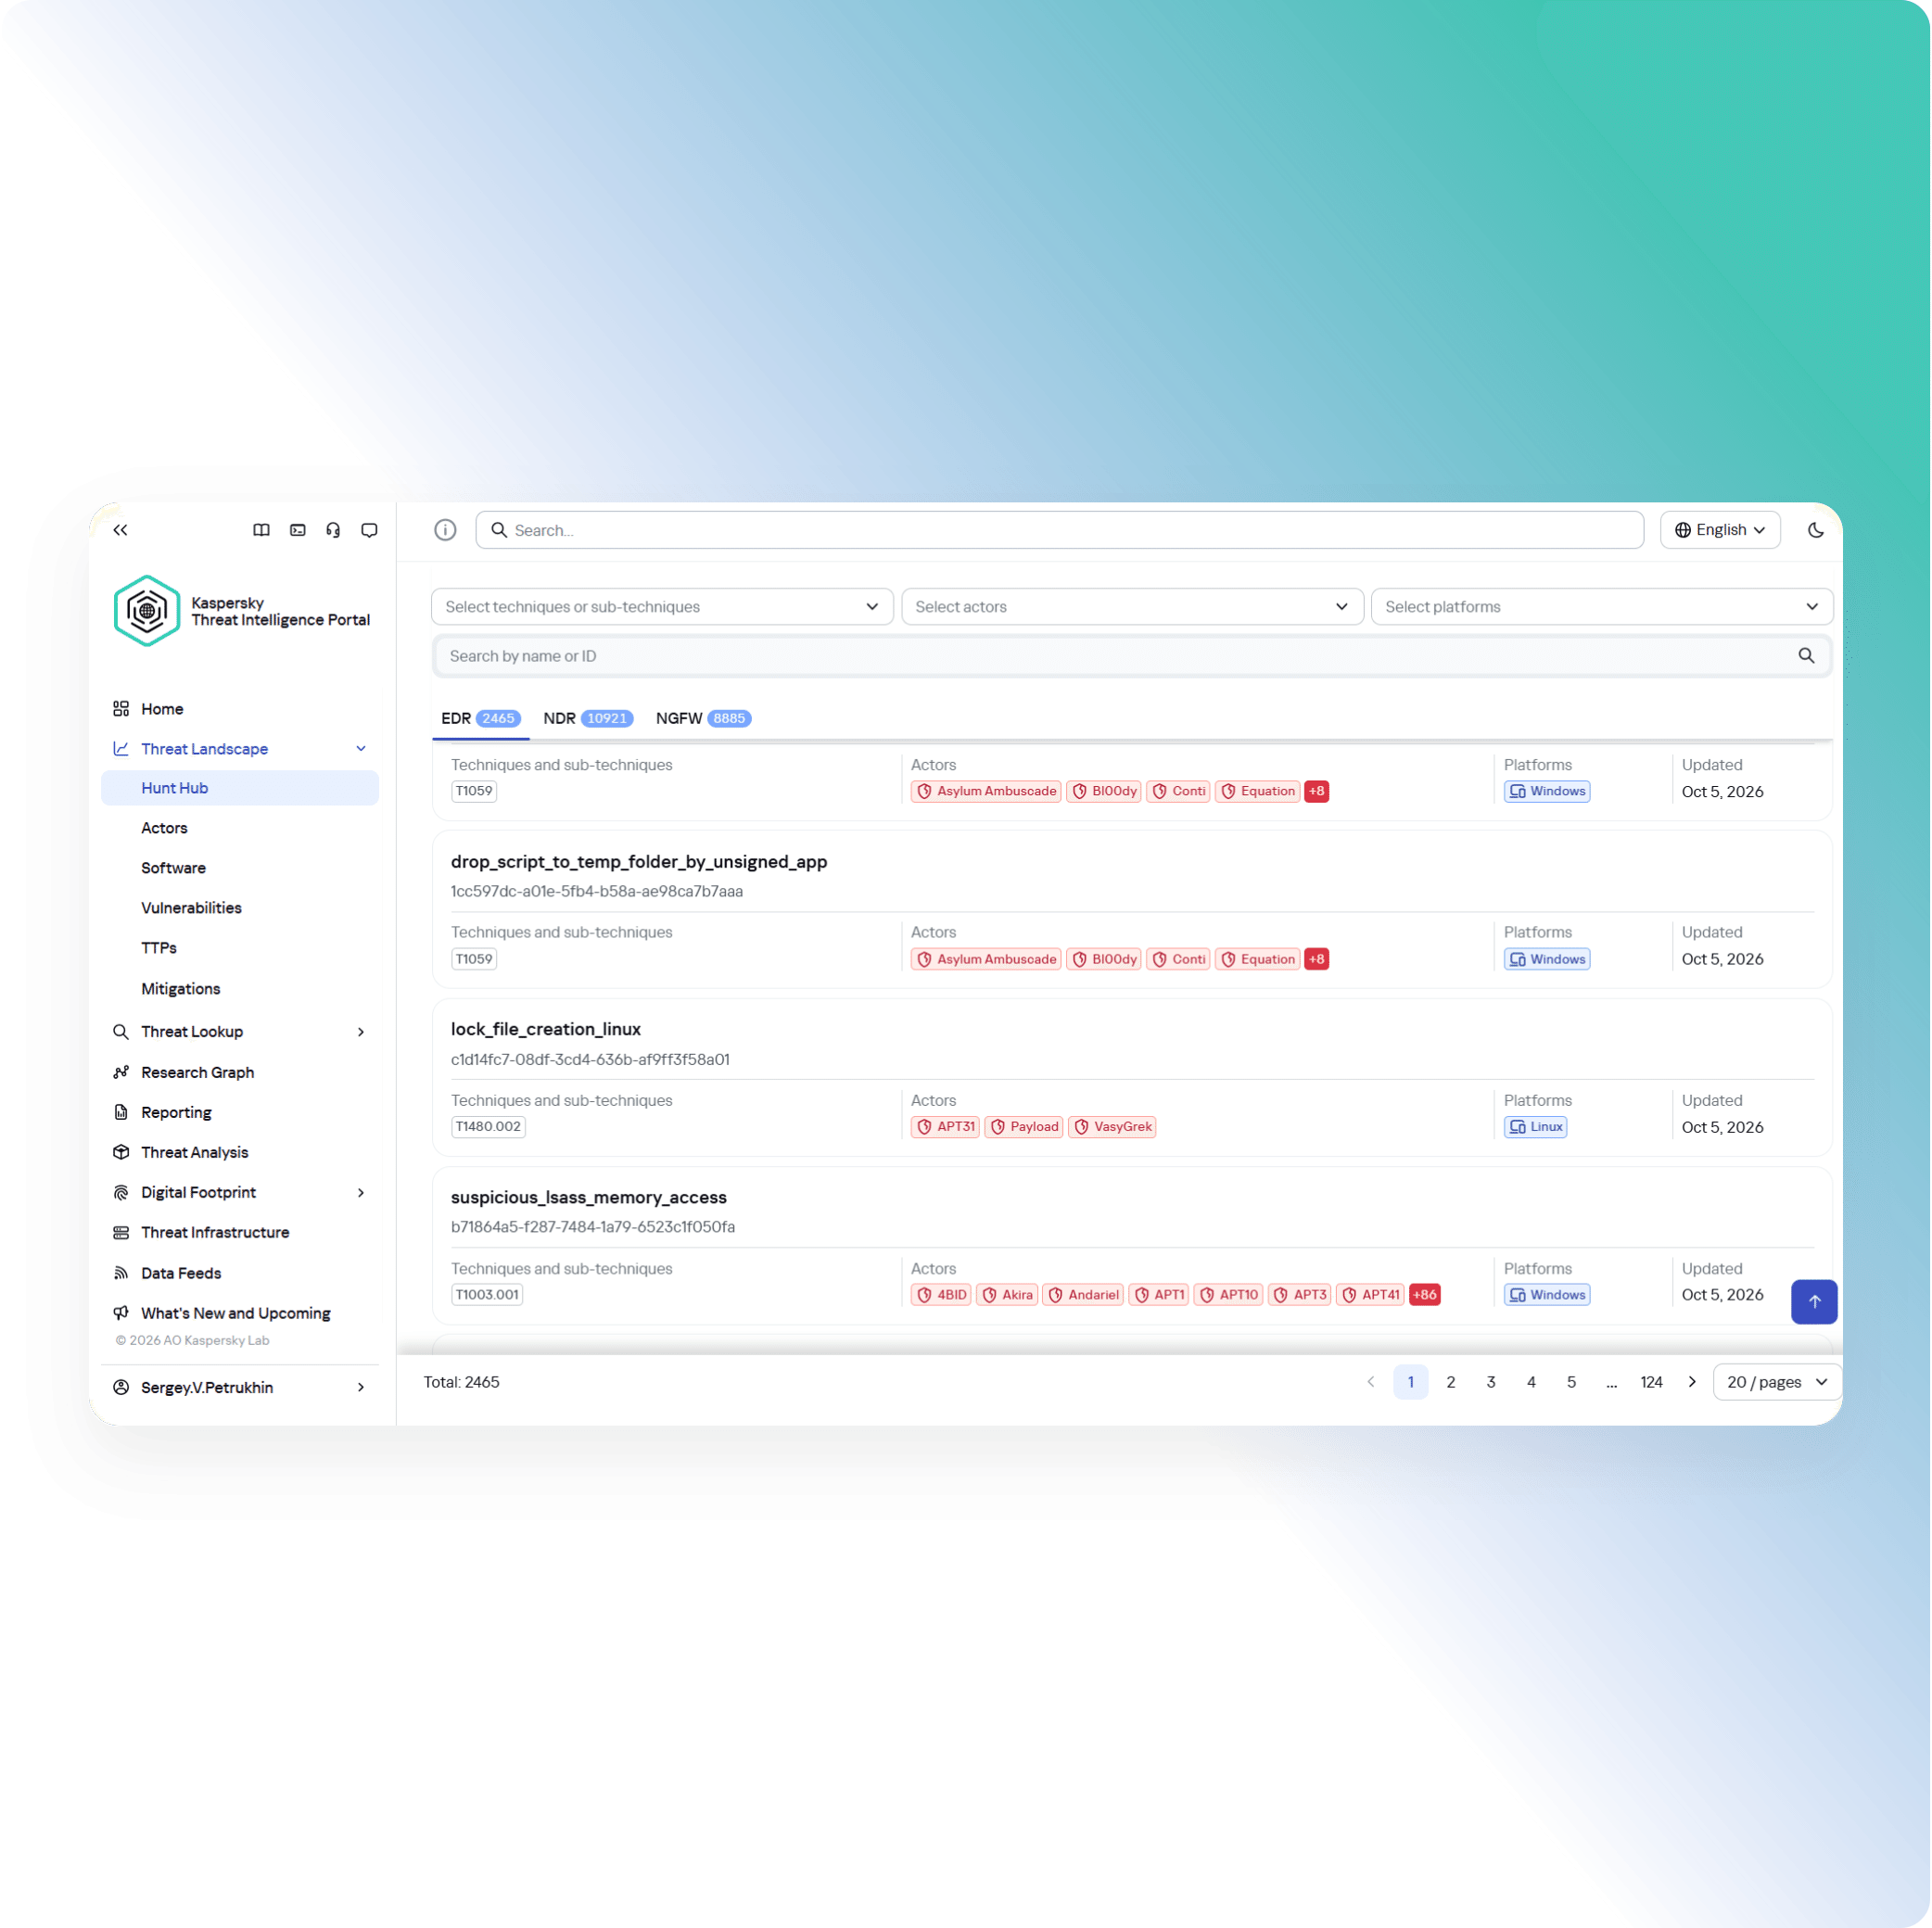
Adversary Tracking
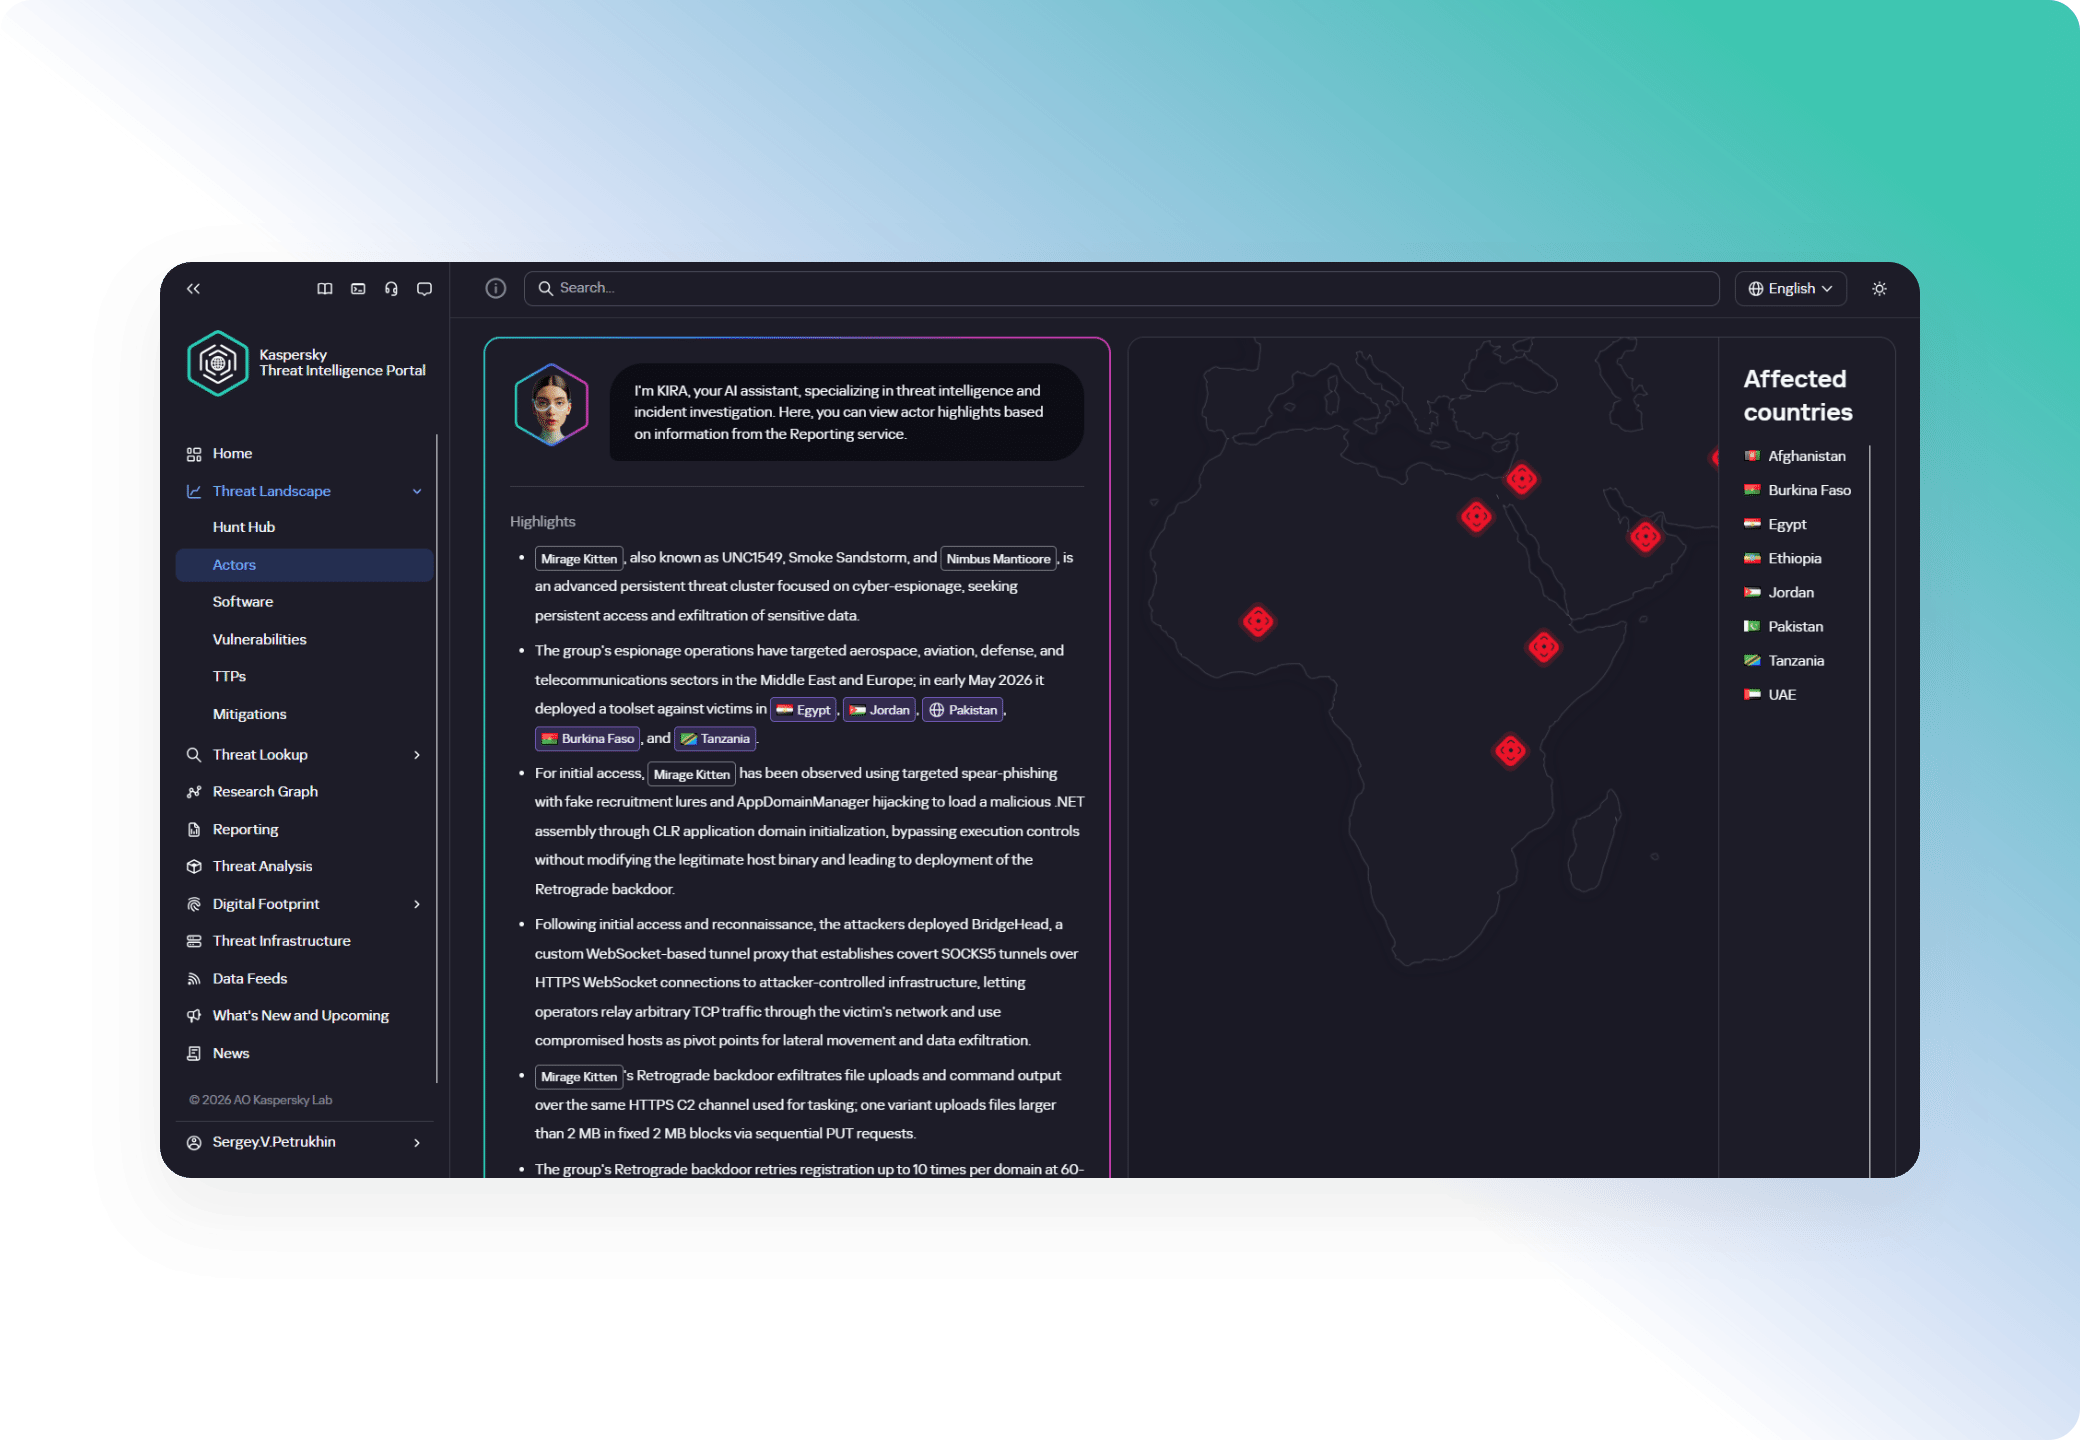
Understand which threat actors are most relevant to your organization and track their activity, capabilities and campaigns.
- Identify relevant adversaries – discover threat actors and campaigns targeting your industry and region
- Track attacker activity – follow related infrastructure, malware and indicators
- Capabilities and intent – access expert analysis of APT, crimeware and other sophisticated threat actors
- Build an adversary view – connect campaigns and attacker activity to your organization’s specific threat environment
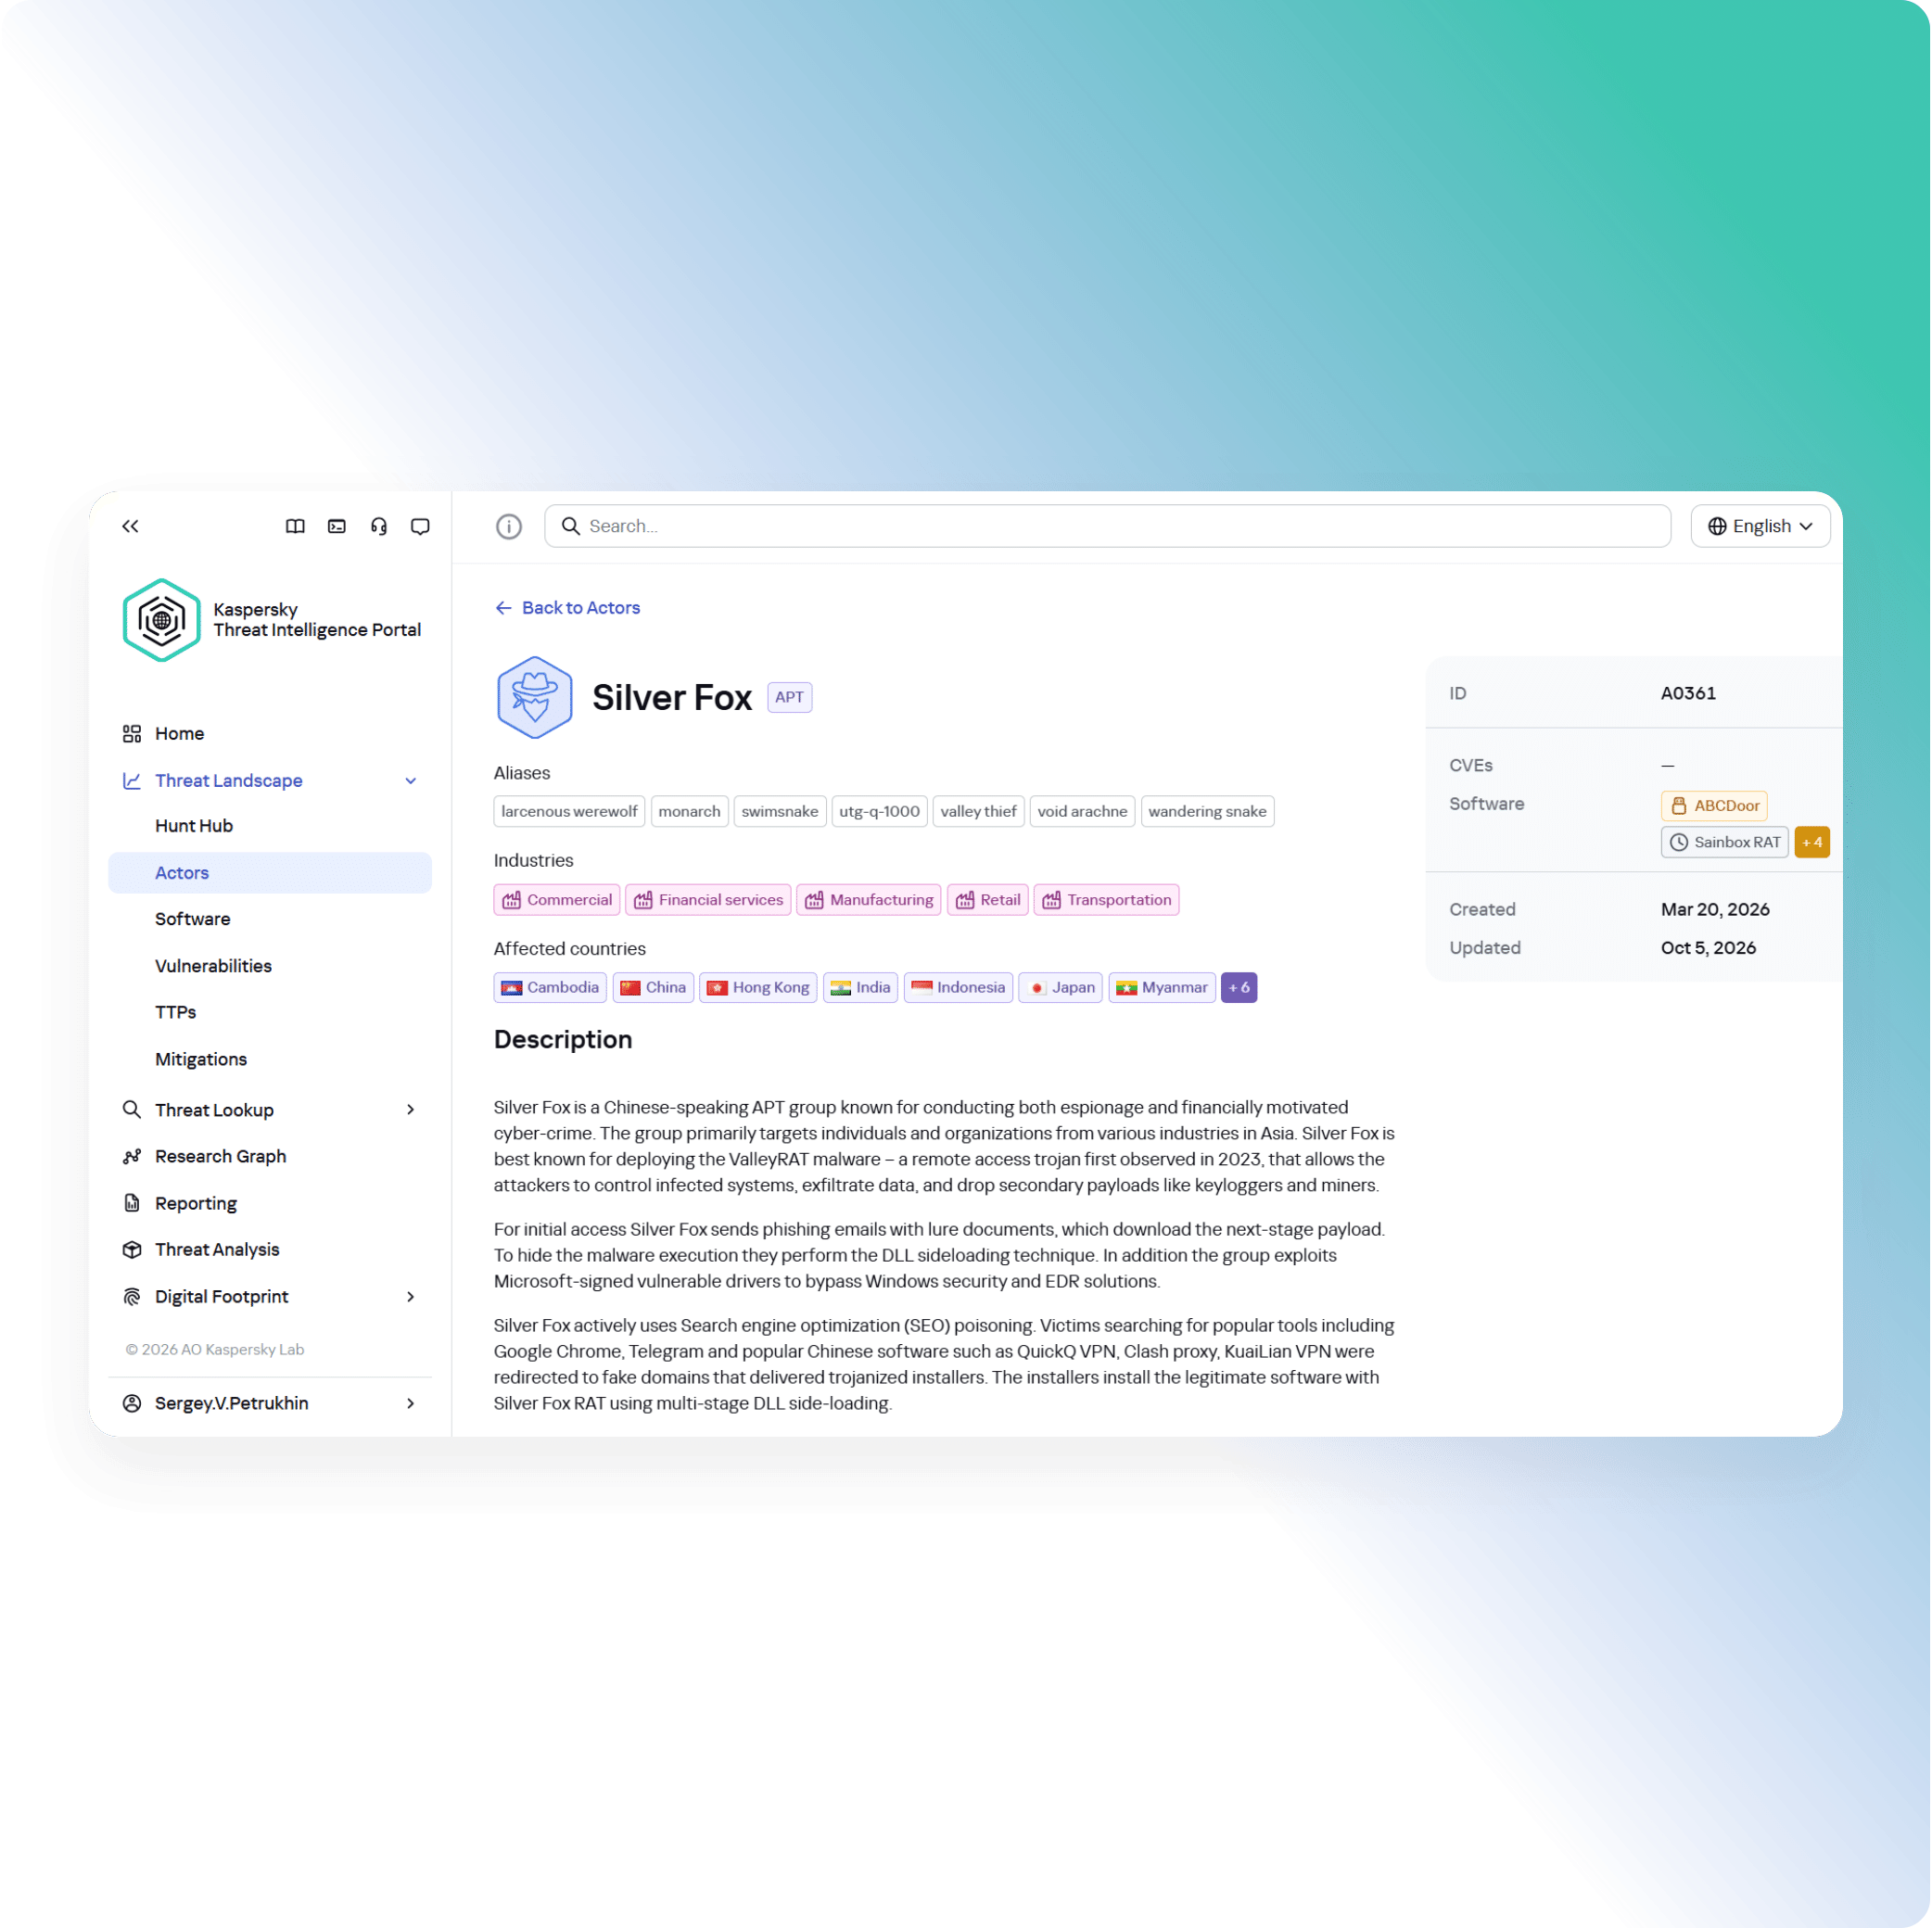
Digital Risk & Brand Protection
Discover and investigate threats targeting your digital presence, brand and externally exposed assets.
- Discover exposed assets – identify external assets, misconfigurations and exposed services
- Find compromised data and accounts – monitor the deep and dark web for leaked data and compromised credentials
- Detect brand abuse – identify impersonation, phishing, fraudulent resources and unauthorized use of your brand
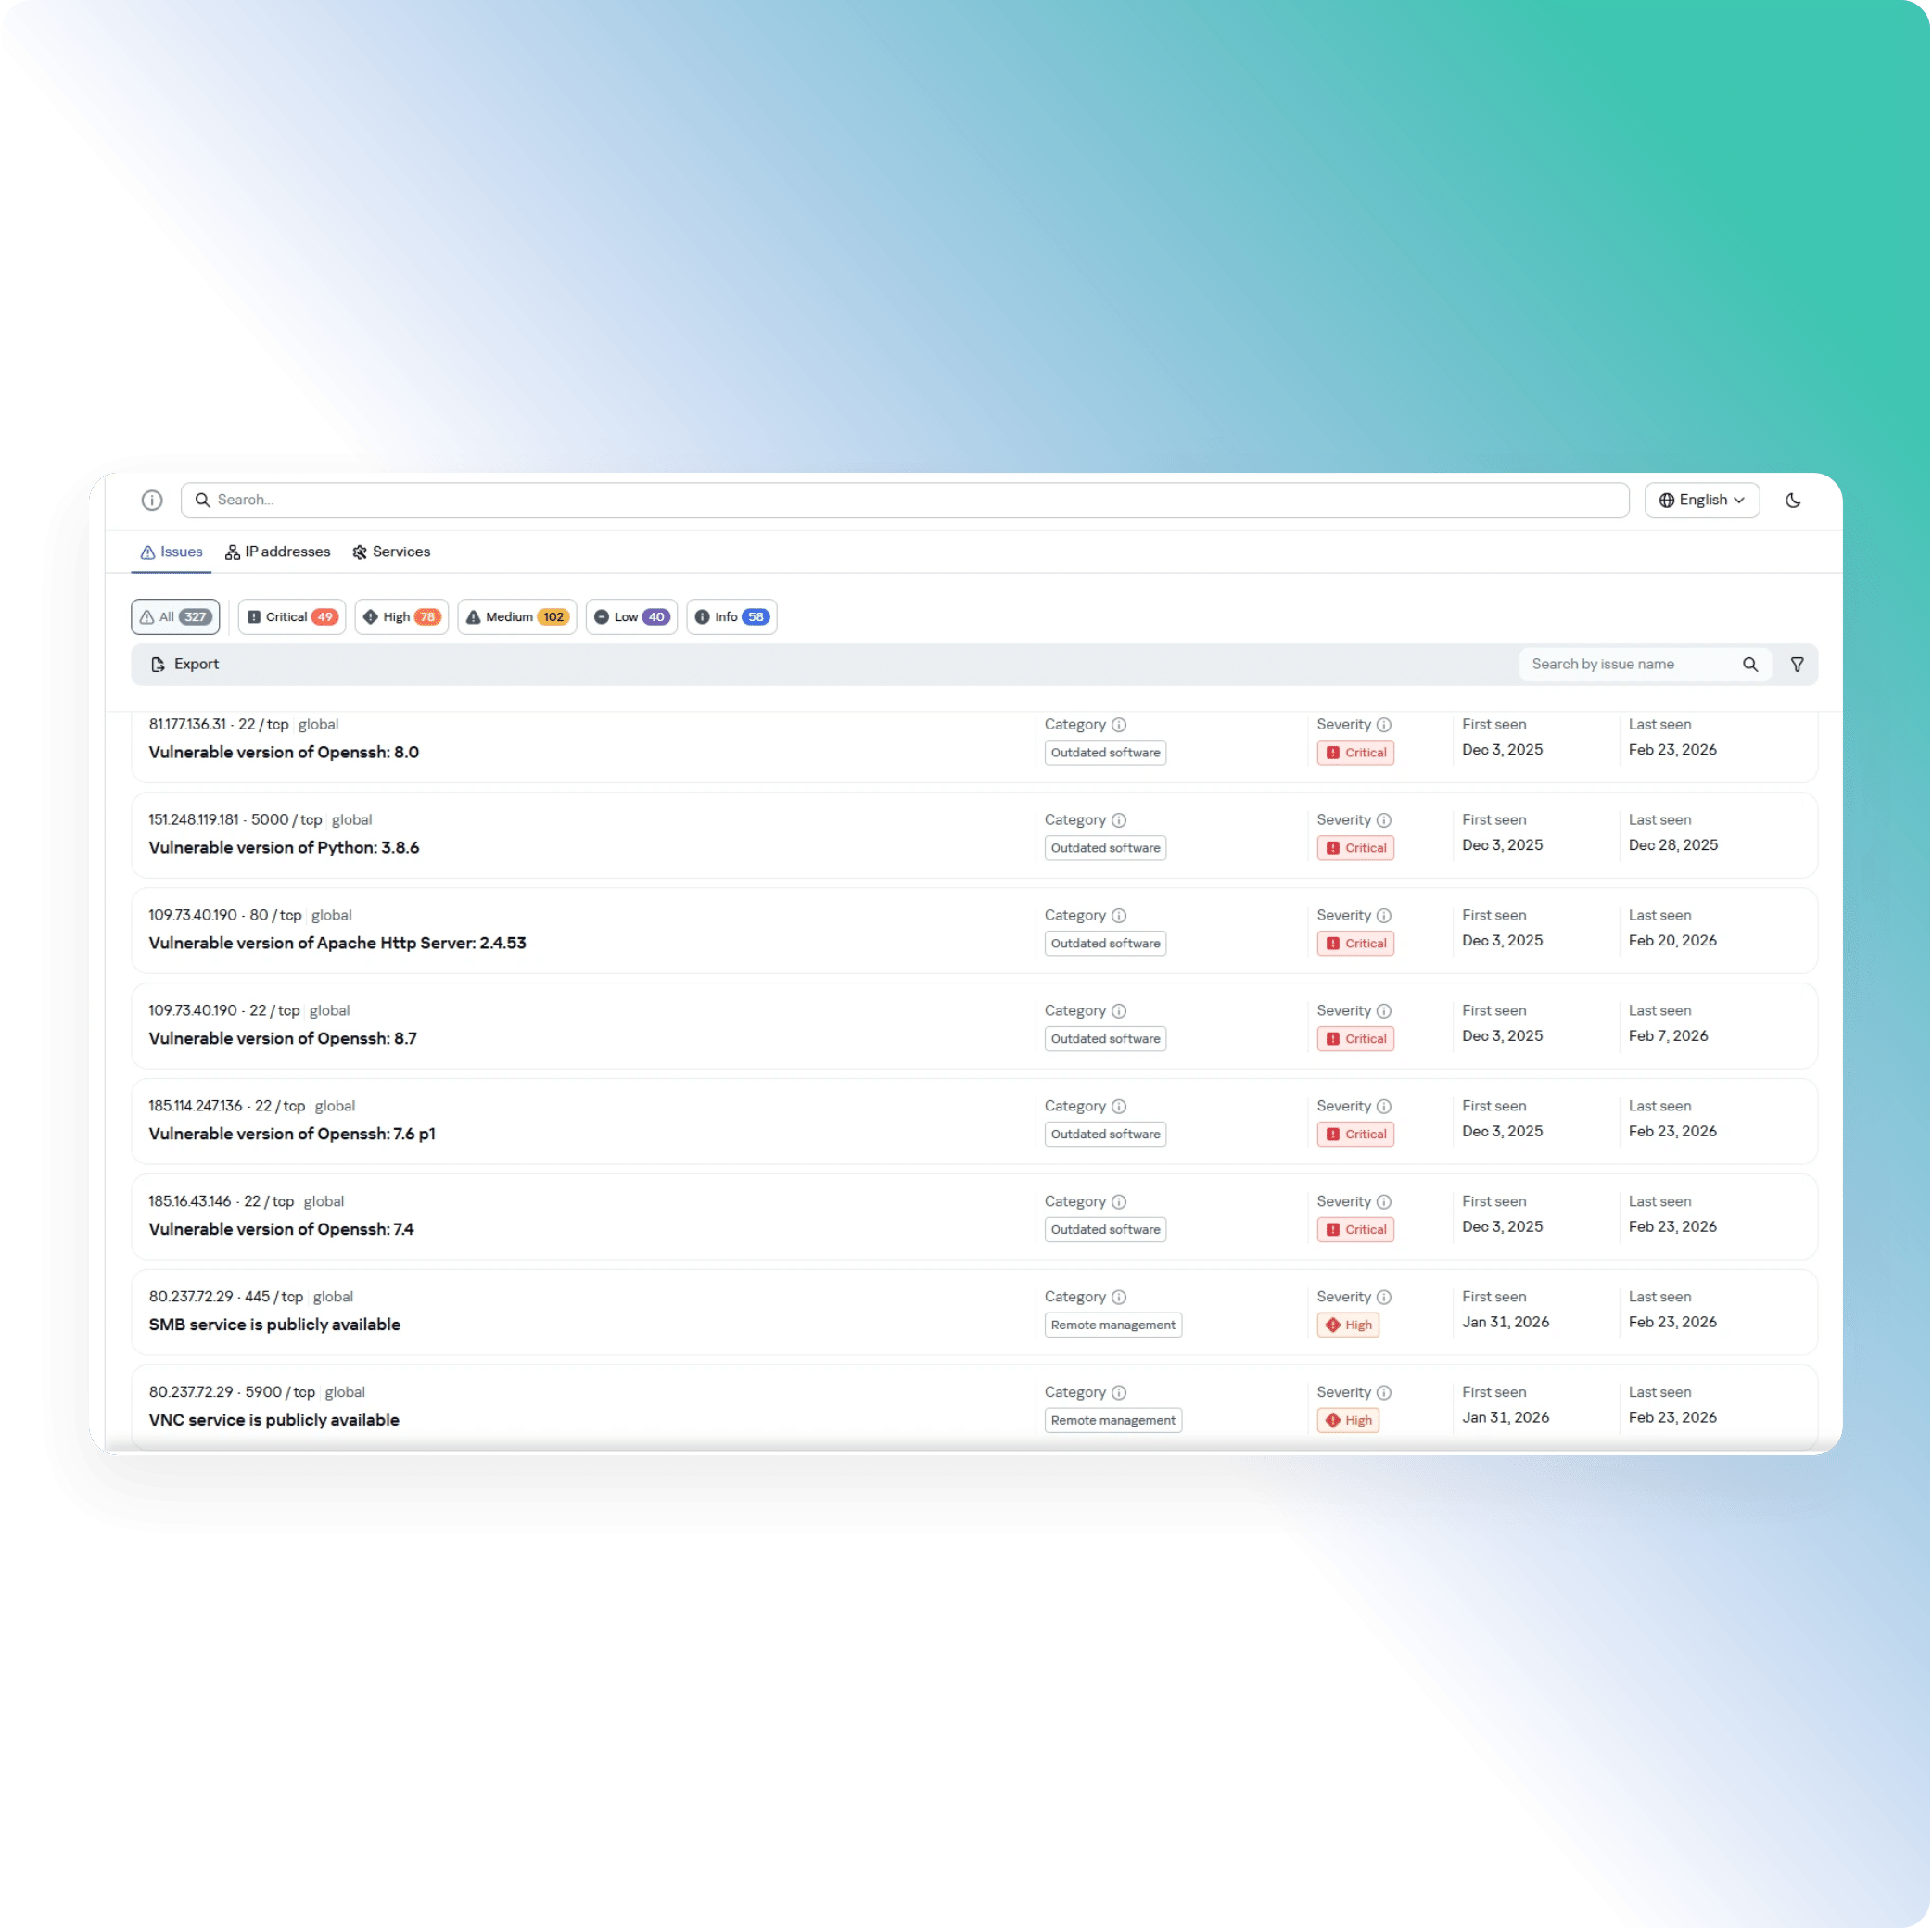
Strategic Decision Support
Turn threat intelligence into strategic insight to help prioritize risk, investment and security initiatives.
- Define your threat environment – understand the threats and adversaries most relevant to your organization
- Identify emerging risks – track trends, attacker activity and developments that could affect your industry
- Understand sophisticated threats – access expert analysis of major APT, crimeware and ICS campaigns
- Validate strategic concerns – conduct deeper investigations into specific threats when needed
- Assess broader business exposure – incorporate external and reputational risks into your security decisions
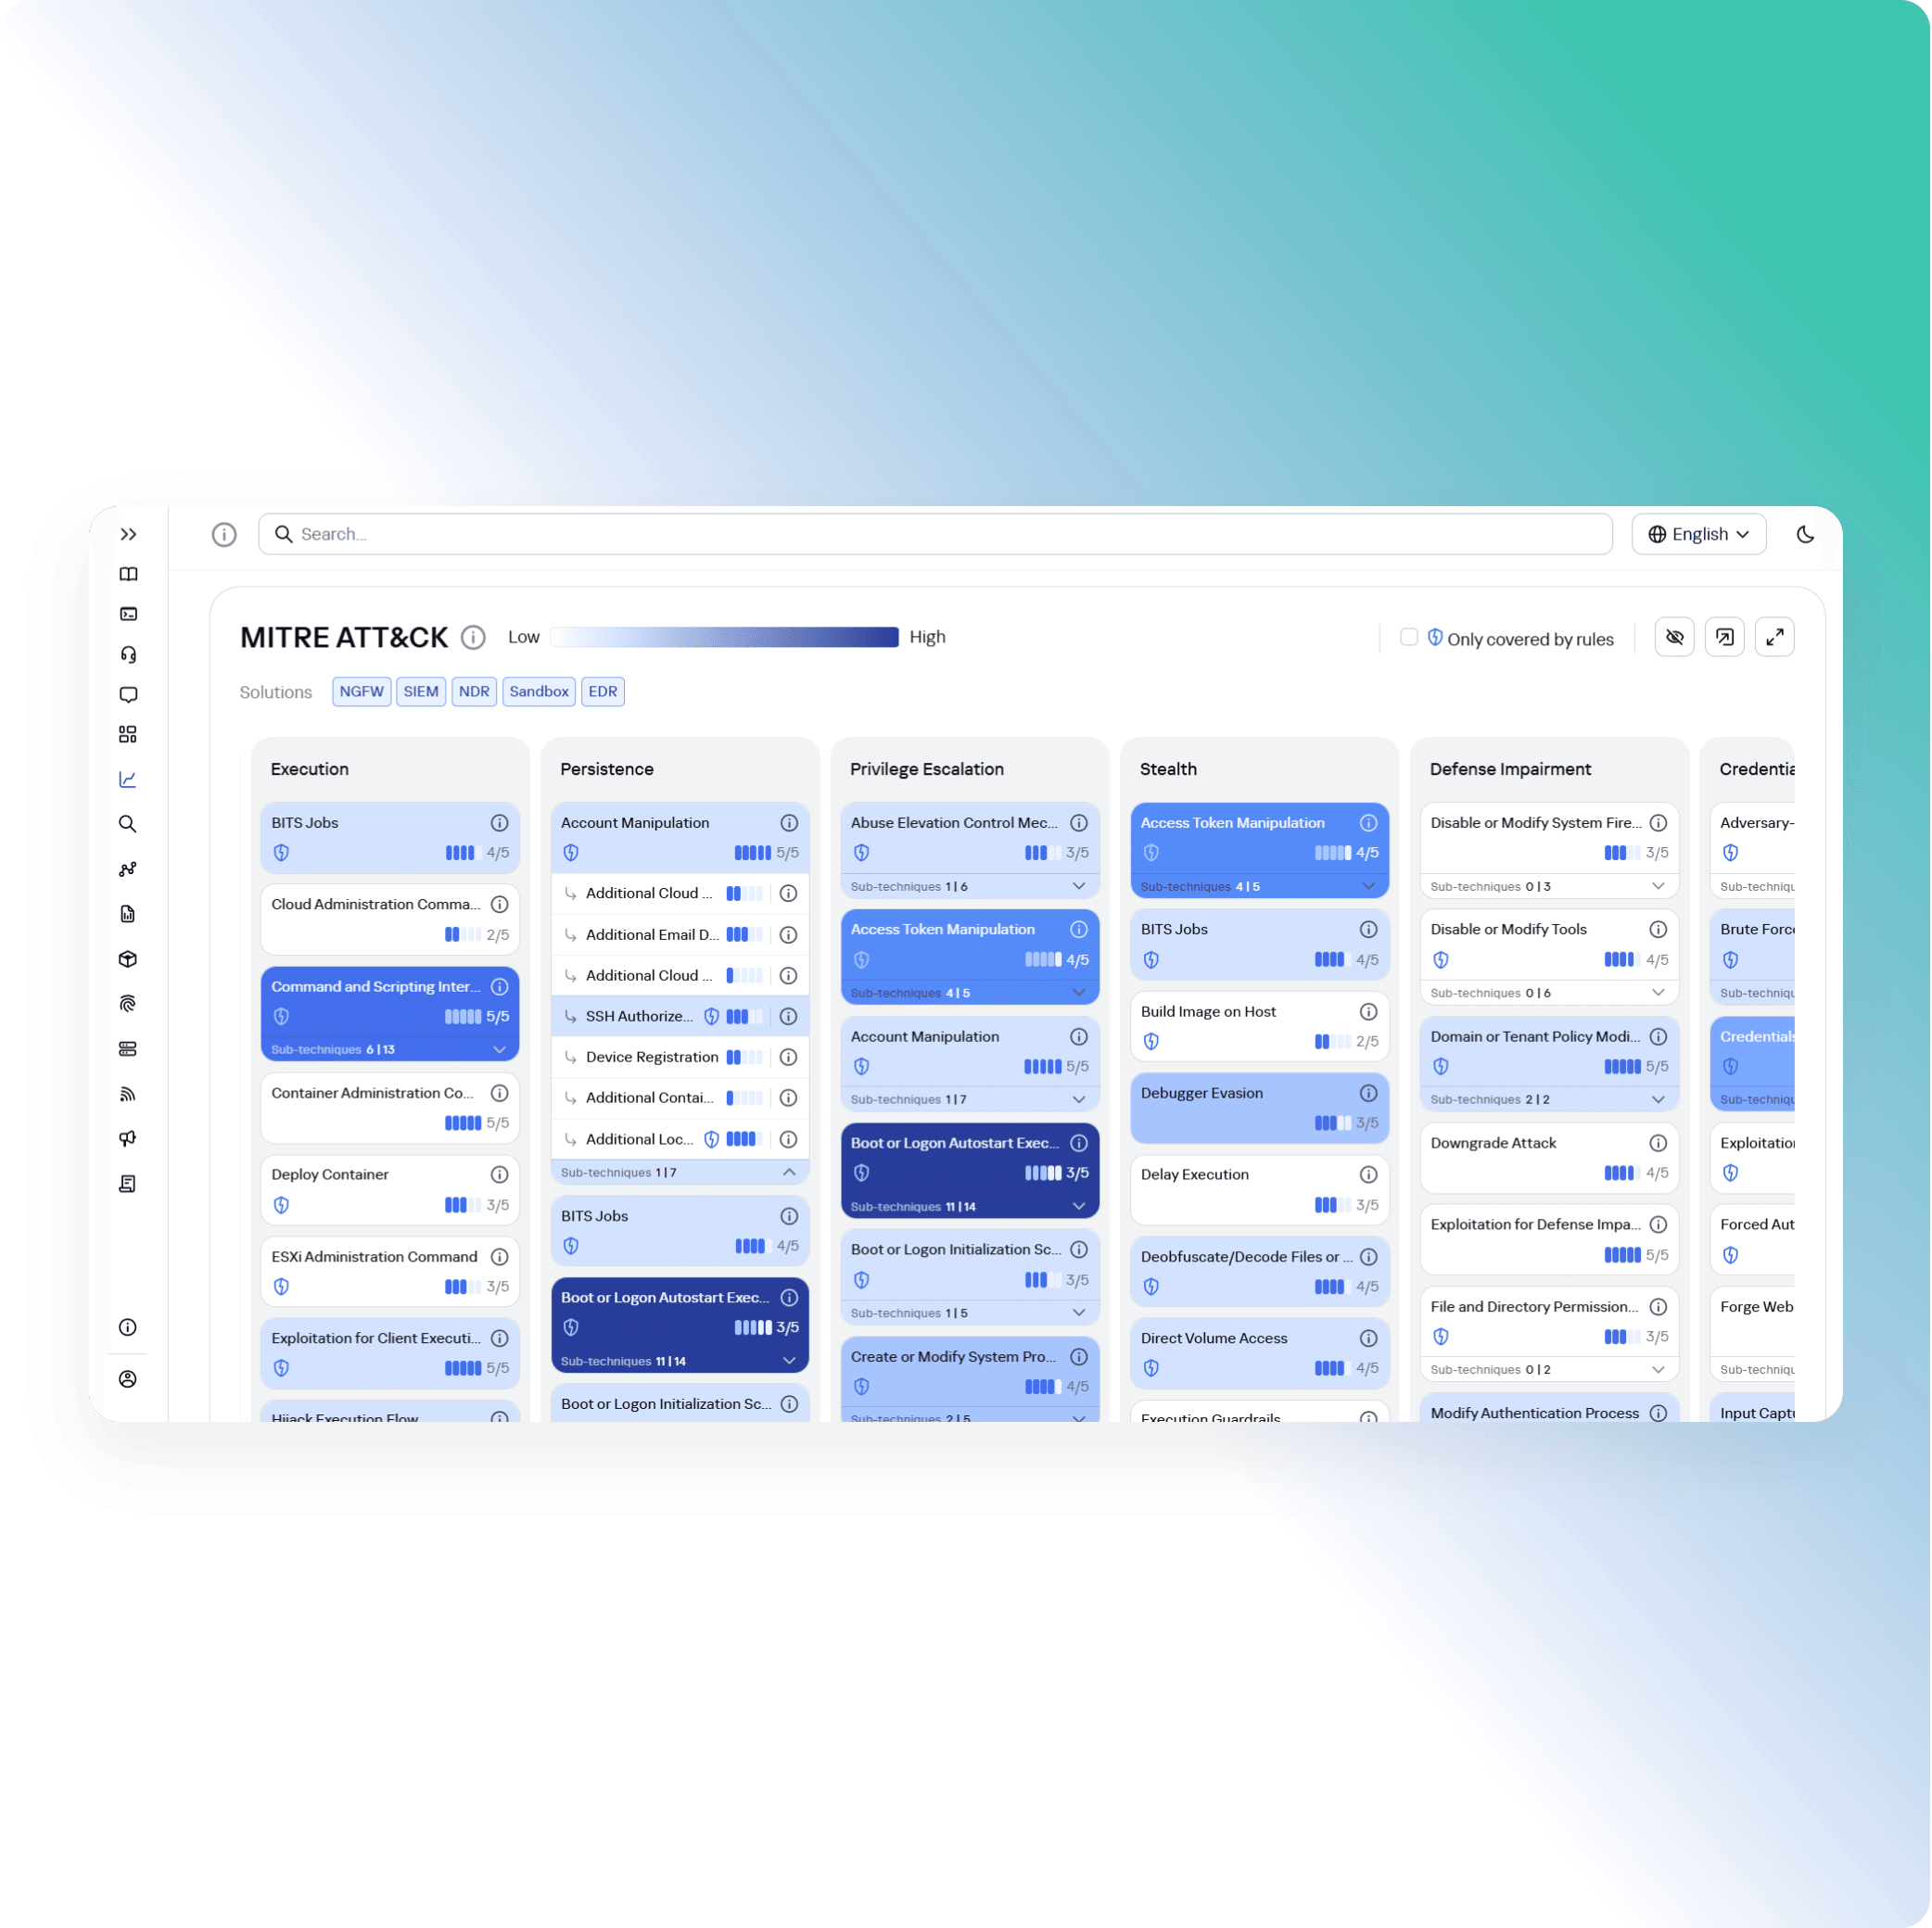
Most trusted. Most awarded.


Clear value for every security role
How Kaspersky TIP supports different security teams and specialists across threat intelligence workflows.

C-level
Gain a clearer view of external risk, justify security investment against the actual threat landscape and improve the effectiveness and value of your existing security stack.

SOC L1/L2
Instantly enrich every alert with relevant context, filter false positives automatically and accelerate triage – reducing repetitive workload and analyst fatigue.

SOC L3 and threat hunters
Investigate complex threats in greater depth, link activity to known APT groups, analyze suspicious samples securely in a sandbox and access unique research and insights from Kaspersky experts.
BENEFITS
What sets the Kaspersky Threat Intelligence Portal apart


RELATED KNOWLEDGE
Learn more about Threat Intelligence and the latest cyber incidents
Request access to Kaspersky Threat Intelligence Portal
Experience Kaspersky Threat Intelligence Portal and explore how our threat intelligence can support your day-to-day security operations. Complete the form below to request trial access. Your request will be reviewed by our team, and once approved, you’ll receive an email with instructions on how to access the portal.